Kein VPN-Dienst – das Protokoll, auf dem jeder kommerzielle VPN aufbauen möchte, und das am besten belegte Tunnelprotokoll überhaupt. Du bist der Anbieter: Erzeuge Schlüssel, führe wg-quick auf einem 5-Dollar-VPS oder einem Raspberry Pi aus, und es gibt kein Unternehmen, das vorgeladen werden kann, keine Datenschutzrichtlinie, der du vertrauen musst, und keine Logs, es sei denn, du schreibst sie selbst. Die Belege sind selbst für Open-Source-Verhältnisse ungewöhnlich: etwa 4.000 Codezeilen gegenüber 600.000 bei OpenVPN+OpenSSL, vier unabhängige formale bzw. Sicherheitsanalysen (symbolischer Beweis mit Tamarin, eCK-komputationaler Beweis, INRIA-CryptoVerif-Beweis des gesamten Protokolls inklusive Datentransport, und das ProVerif-Noise-IK-Modell), maschinell verifizierter Curve25519-Code, eine saubere externe Prüfung vor Version 1.0 sowie Aufnahme in den Mainline-Linux-Kernel seit 5.6 (Zusammenführung im Januar 2020, Veröffentlichung im März 2020). Die Kompromisse sind strukturell, nicht zufällig: ausschließlich UDP mit einem fingerabdruckbaren Handshake (Russland begann 2024 mit der Blockade von OpenVPN/WireGuard-Verbindungen; AmneziaWG existiert genau aus diesem Grund), das Schlüsselmanagement liegt vollständig bei dir, prozessbasiertes Split-Tunneling ist so umständlich, dass Nutzer auf HN es als gravierendes Usability-Problem bezeichnen, und der Windows-Client ist der Treiberunterzeichnung von Microsoft ausgeliefert (eine Beendigung der Signierung im April 2026 zwang zu einem Notfall-Release). Es wird dich außerdem niemals vor deinem eigenen VPS-Anbieter oder deinem Heim-ISP anonymisieren – eine selbstgehostete Exit-IP ist lediglich deine eigene Identität an einem neuen Ort.
AuditOpen Source4 rote FlaggenFakten verified - live-fetched 2026-11-03: wireguard.com (home, install, protocol, formal-verification, repositories), IACR ePrint 2018/080, noiseexplorer.com IK analysis, Wikipedia, Ars Technica (2018 review + 2020 kernel-5.6 report), Cloudflare BoringTun blog, GitHub API metadata for WireGuard/wireguard-tools, HN Algolia comment and story search, and the r/WireGuard arctic-shift archive (body-search endpoint returned HTTP 400; the plain listing endpoint was used instead). wireguard.com/papers/ returned HTTP 403 to our fetcher and the whitepaper PDF is not text-fetchable, so whitepaper facts are cited from the project's formal-verification page. Tailscale's 'why WireGuard' post 404s at its old URL; hal.inria.fr sits behind an Anubis bot-check.
The formal proofs cover the HANDSHAKE and primitives, not your deployment: Dowling-Paterson prove a minimally modified variant (the eCK paper notes WireGuard's key confirmation makes the exchange 1.5-RTT and rules out a clean proof of key indistinguishability), and every proof assumes you did key distribution correctly - the code you run and the keys you manage sit outside all of it
Identity hiding is conditional: per the operator's own formal-verification page, when the responder's static key is compromised WireGuard does not achieve identity hiding - the initiator's identity is protected, the server's is not
State-level censorship treats vanilla WireGuard as protocol enemy #1: Russia blocked OpenVPN/WireGuard in 2024 (HN), and 2026 reporting from Iran documents WireGuard tunnels with limited success against heavy filtering (Wikipedia/Iran International) - if censorship resistance matters, the core protocol alone is not enough
+1 weitere rote Flaggen - vor der Anmeldung aufklappen
Single-maintainer bus factor: the project, codebase and trademark belong to one person (Jason A. Donenfeld / ZX2C4); official GitHub repos are mirrors with issues disabled, bug reports go to a mailing list - healthy for focus, fragile for succession
Review
Entwurf von Qwen3, faktengeprüft von der vpnvergleich-Redaktion · Review-Version 7 · Text aktualisiert 2026-11-03 · Fakten Stand 2026-11-03 · wie wir verifizieren
Ehrlichkeits-Hinweis: wir haben keine eigenen Tests zu Self-hosted WireGuard on a cheap VPS gelaufen (Leak-Tests, Tempo, Kill Switch). Alles auf dieser Seite ist quellbasierte Meta-Recherche mit datierten Links. Sobald wir testen, erscheinen die Ergebnisse hier und im Änderungsprotokoll.
Overview
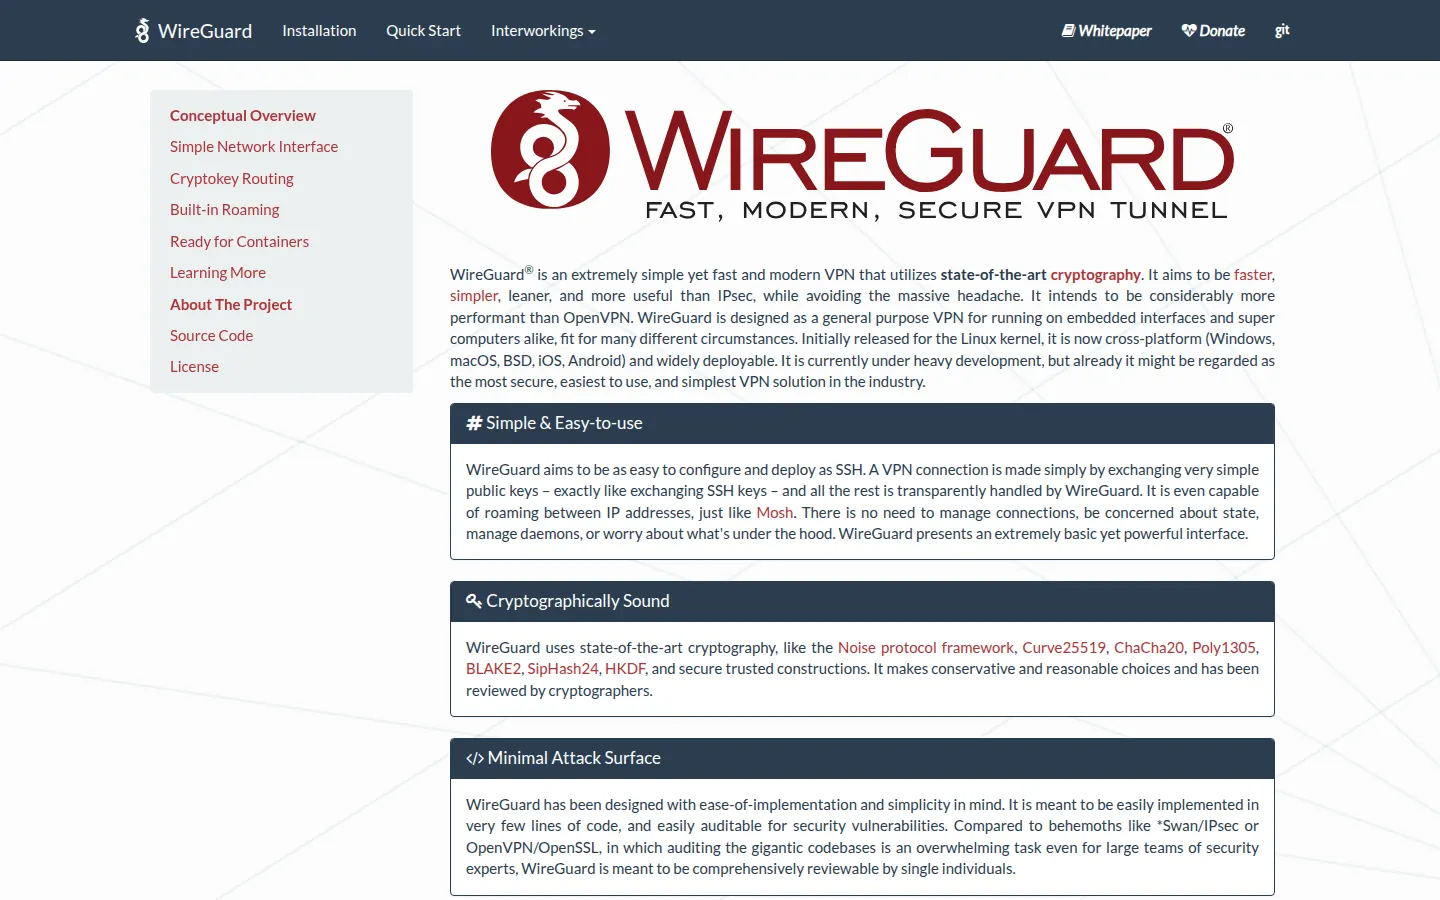
Self-hosted WireGuard on a cheap VPS homepage - live capture 2026-09-29
Self-hosted WireGuard on a cheap VPS isn't a commercial VPN - it's you running the protocol on infrastructure you control. There's no provider to trust, no privacy policy to parse. You are the operator: generate keys, deploy on a $5/month VPS or a Raspberry Pi, and eliminate third-party logging by design. The caveat? You inherit full responsibility for security, uptime, and key management.
Logging & privacy
WireGuard logs nothing by design - the protocol is stateless, and the reference tools don’t persist connection data. Any logging occurs only if you configure it on your own server. There’s no privacy policy to audit because there’s no central entity. The evidence isn’t a corporate audit but formal verification: symbolic (Tamarin), computational (eCK, CryptoVerif), and machine-checked proofs confirm handshake security, forward secrecy, and key agreement. However, identity hiding fails if the server’s static key is compromised. Jurisdiction is irrelevant - there’s no operator to subpoena.
Pricing & the renewal trap
The WireGuard software is free (GPL/MIT/BSD-licensed); you pay only for the infrastructure - typically around $5/month for a VPS, or less (some HN users report ~$2/year for minimal boxes). There is no renewal trap because there is no billing - no intro price, no renewal, no contract. You control the machine, so costs depend entirely on your hosting choice. The derived_pricing fields are null because this is not a subscription service.
Features & performance
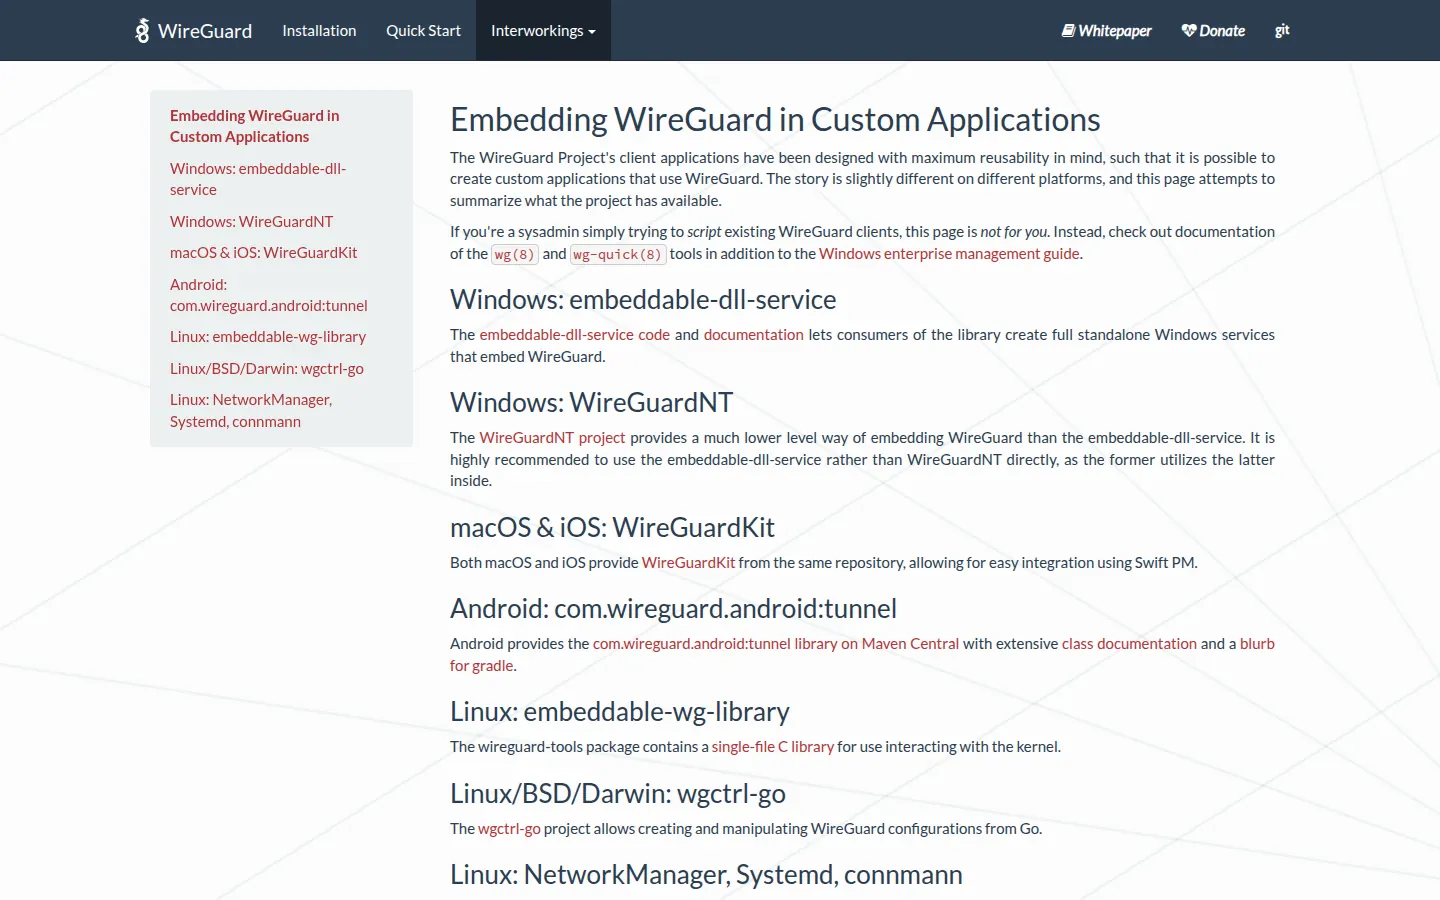
Self-hosted WireGuard on a cheap VPS apps / download page - live capture 2026-09-29
WireGuard uses its own protocol (Noise_IKpsk2 over UDP) with ChaCha20, Curve25519, and BLAKE2s. It has no built-in kill switch, multihop, or obfuscation. Split tunneling is possible but clunky on some platforms. It supports all major OSes and routers. There are no central servers - your deployment defines performance. Independent reports show multi-gigabit throughput on capable hardware. P2P and streaming aren’t direct features, but the tunnel can carry any IP traffic. Performance is high due to kernel integration and minimal code (~4,000 lines), but we have not run our own tests.
Ownership & track record
WireGuard was created and is maintained by Jason A. Donenfeld (ZX2C4), who holds the copyright and trademark. It has no corporate owner. The project is hosted on GitHub as mirrors only; bug reports go to a mailing list. Red flags include a single maintainer (bus factor risk), no issues on official repos, and dependency on third parties (e.g., Microsoft’s driver signing, which caused an emergency Windows release in April 2026). Despite this, it has a decade of strong reputation: Linux kernel inclusion (5.6, 2020), formal proofs, and endorsements from Torvalds and Senator Wyden.
Censorship resistance
Vanilla WireGuard has no obfuscation - the handshake is simple and easily fingerprinted over UDP. Russia began blocking OpenVPN/WireGuard in 2024, and Iran’s 2026 filtering limited its effectiveness. It is not suitable for high-censorship regions without modification. Third-party forks like AmneziaWG add obfuscation to resist DPI, but the core protocol alone is not censorship-resistant.
Verdict
If you self-host, WireGuard is the gold standard: minimal, fast, and backed by more cryptographic evidence than any commercial VPN. It’s ideal for homelabbers, developers, and privacy-focused users who already run infrastructure. But it’s not turnkey - expect to manage keys, firewalls, and updates. There’s no money trail: WireGuard doesn’t pay review sites, and it has no affiliate program.
++ Was hält stand
Formal auf vier unabhängige Arten verifiziert – Tamarin symbolischer Beweis, eCK berechenbarer Beweis, INRIA CryptoVerif-Beweis des gesamten Protokolls inklusive Transportdaten-Nachrichten, ProVerif Noise-IK-Modell (offizielle Formalverifikationsseite, IACR ePrint, Noise Explorer – alle abgerufen 2026-11-03)
Etwa 4.000 Codezeilen gegenüber 600.000 für OpenVPN+OpenSSL – Angriffsfläche, die eine Einzelperson tatsächlich überprüfen kann (Ars Technica 2018, live abgerufen)
Seit Kernel 5.6 im Linux-Hauptentwicklungsstrang (eingefügt Jan 2020, ausgeliefert März 2020) – erstklassiges Kernelmodul, keine DKMS-Neukompilierungen (Ars Technica 2020)
Zustandslos: Es existieren keine Logs, es sei denn, der Betreiber konfiguriert sie; kein Anbieter bedeutet kein Ziel für Vorladungen und keine Richtlinie, an der man zweifeln müsste (Protokolldokumentation des Betreibers)
Läuft auf allem: offizielle Pakete für Windows/macOS/iOS/Android/BSDs/OpenWRT sowie eine Go-Userspace-Implementierung; HN-Nutzer betreiben Peers auf 128-MB-RAM-VPS-Systemen (Installationsseite + HN-Nutzerstimmen abgerufen 2026-11-03)
Sofortige Verbindungsaufnahme: etwa 100 ms Verbindungsaufbau gegenüber 8+ Sekunden bei OpenVPN im Test von Ars Technica (2018 Review)
Linus Torvalds über den Code: Im Vergleich zu OpenVPN und IPsec sei es 'ein Kunstwerk' (LKML, zitiert im abgerufenen Ars-Review)
-- Worauf du achten solltest
Nur UDP und trivial identifizierbar – keine Verschleierung im Kern; Russland begann im Januar 2024 mit der Sperrung von OpenVPN/WireGuard-Verbindungen (439-Beiträge-HN-Thread), und AmneziaWG ist ein kompletter Fork, der genau dies beheben soll
Schlüsselverwaltung liegt ganz bei dir: Erzeugung, Rotation, Verteilung und Pflege der AllowedIPs pro Peer, ohne Dashboard in wg-quick
Ein VPN auf einen Unterprozess zu beschränken, ist umständlich – HN: 'WireGuard hat massive Usability-Probleme deswegen'; Workarounds wie wireproxy existieren (HN, Okt 2026)
Die Windows-Verteilung hängt von der Microsoft-Code-Signierung ab – im April 2026 sperrte Microsoft das Signierkonto, und WireGuard veröffentlichte einen Notfall-Release (HN-Thread 47719942)
Die Port-Qualität variiert außerhalb von Linux: Kernel-Modus-Unterstützung wurde 2021 aus FreeBSD 13.0 entfernt, bevor sie über pfSense-Pakete wieder eingeführt wurde (Wikipedia, abgerufen 2026-11-03)
Kein Wert für Geo-Entsperrung: Deine Ausgangs-IP ist deine eigene VPS-/Heim-IP, daher keine Änderung der Streaming-Kataloge, keine gemeinsam genutzten sauberen IPs
Preis-Realitätscheck
Einführungspreis
ca. 4,40 € /mo
Hinweise
Das Protokoll und alle Referenzimplementierungen sind kostenlos. Die Angabe von 5 USD ist eine Einordnung dieser Seite: ein günstiger VPS (etwa 5 USD/Monat) oder ein Raspberry Pi zu Hause reicht aus, um einen eigenen WireGuard-Server zu betreiben. HN-Nutzer (abgerufen 2026-11-03) betreiben WireGuard-Peers regelmäßig auf extrem günstigen VPS-Angeboten – einer beschreibt ein paar Dollar pro JAHR für eine 128-MB-RAM-Box mit Alpine, die als WireGuard-Peer sowie für eine kleine Website dient.
Der Geldfluss - was Testportale mit dieser Empfehlung verdienen
Affiliate-Status noch nicht verifiziert
Sollten wir dieses Programm joinen, wird jeder Link hier rel="nofollow sponsored" und läuft über /go/. Bis dahin zeigen unsere Links direkt auf die Anbieter-Website, ohne jegliches Tracking. Die Ranking-Logik kann Affiliate-Felder physisch nicht lesen - hier der Beweis.
On the website
Captured by our screenshot bot from the live site (or its public archive). A capture is evidence of what the page showed at capture time - not an endorsement.
Self-hosted WireGuard on a cheap VPS homepage - live capture 2026-09-29Self-hosted WireGuard on a cheap VPS apps / download page - live capture 2026-09-29
Bevor du zahlst: prüfe den Verlängerungspreis, das Erstattungsfenster und ob ein günstigerer oder Gratis-Weg deinen Anwendungsfall abdeckt - die ehrliche Checkliste.
Stand unserer Prüfungen: 2026-11-03. Self-hosted WireGuard on a cheap VPS erreicht 4/10 in unserem gewichteten Review. Wir haben 4 rote Flaggen vermerkt (oben aufgelistet). Nutzerberichte, Eigentum und die Vorfallhistorie sind mit datierten Quellen im Meta-Review unten dokumentiert.
What do I actually get?
You get free, open-source software to create encrypted tunnels. You run it on your own server - no accounts, no data caps, no provider. Everything from key generation to uptime is your responsibility.
What is the renewal price and total 3-year cost?
There is no renewal price. The software is free. Your cost is only the VPS or hardware - around $5/month typically. The three_year_cash_total is null because pricing depends entirely on your hosting choice.
What evidence supports the no-logs claim?
There are no logs because the protocol is stateless and the tools don’t record connections. The evidence isn’t a policy or audit - it’s structural: no operator exists to log. Formal verification confirms cryptographic soundness, but deployment security is yours to maintain.
Does it work in censored countries like China or Iran?
Not reliably. The core protocol has no obfuscation and is easily blocked. Iran and Russia have filtered WireGuard since 2024. Use obfuscated forks like AmneziaWG if censorship resistance is required.
Can I pay anonymously?
There’s no payment at all - the software is free. But your VPS provider may require ID. For anonymity, use a provider that accepts cryptocurrency and doesn’t enforce KYC.
What happens if the project shuts down?
The code is open-source and already in the Linux kernel, FreeBSD, and OpenBSD. Even if development stops, it will remain usable. The main risk is the single maintainer, but the codebase is small and well-understood.
What’s the honest free or cheap alternative?
WireGuard itself is free. For a managed option, consider Mullvad or IVPN - both are independent, audited, and support direct WireGuard profile use. Or run your own on a $5 VPS - cheaper than any commercial plan.
Der Meta-Review: was das Internet über Self-hosted WireGuard on a cheap VPS sagt
Wir erwarten nicht, dass du uns vertraust. Dieser Review ist ein Meta-Review: unten siehst du, was andere Testportale behaupten - mit ihren Interessenkonflikten gekennzeichnet -, was Nutzer auf Reddit und in Foren berichten und wer Self-hosted WireGuard on a cheap VPS wirklich betreibt. Jede Behauptung verlinkt ihre Quelle, damit du sie selbst prüfen kannst.
Was andere Tester sagen (2)
Jede Quelle trägt ein Konflikt-Label aus unserer Testportal-Datenbank. „Affiliate-finanziert“ heißt: Die Seite verdient mit, wenn du kaufst, was sie empfiehlt. Kritische Stimmen nehmen wir bewusst auf.
Fetched 2026-11-03 (HTTP 200): independent hands-on technical review - about 4,000 lines of code vs 600,000 (OpenVPN+OpenSSL) and 400,000 (XFRM+StrongSwan); quotes Linus Torvalds' LKML praise ('compared to the horrors that are OpenVPN and IPSec, it's a work of art'); measured connect time of about 100 ms vs 8+ seconds for OpenVPN on the same path; explains crypto versioning over agility and the optional PSK layer for post-quantum resistance; notes the author got direct Q&A from Jason Donenfeld after publishing configs; 'maybe faster, almost certainly more secure, and definitely a great deal simpler'.
Fetched 2026-11-03 (HTTP 200): engineering analysis from an independent implementer - WireGuard 'built around the Noise Protocol Framework', only a few modern primitives (X25519, ChaCha20-Poly1305, Blake2s); simplicity 'means it is more robust than old, unmaintainable codebases, and can also be implemented relatively quickly'; Cloudflare benchmarked wireguard-go far below the kernel module and chose Rust for memory safety; 'we believe it has a chance of being the defacto standard for VPN-like technologies going forward'.
Was Nutzer sagen (4)
Reddit, Foren, HN - paraphrasiert und verlinkt, nie aus dem Kontext gerissen. Anekdoten, keine Beweise - aber Erstattungsbeschwerden und Leak-Reports sind das beste Frühwarnsystem, das dieser Markt hat.
Fetched 2026-11-03 (HTTP 200): 11,449 matching comments. Recent 2026 voices span the self-host framing (a 2-dollar-a-year VPS as a WireGuard peer; '$0 for Wireguard'), protocol praise ('the simplicity. A small codebase can implement it'), usability criticism (per-subprocess scoping, wireproxy workaround), WireGuard-as-best-practice for admin interfaces, and providers being selected for accepting a plain WireGuard profile.
Fetched 2026-11-03 (HTTP 200): 1,011 matching stories - the milestone threads: 'WireGuard is now in Linus' tree' (982 pts, 278 comments, Jan 2020), 'WireGuard 1.0 for Linux 5.6' (768 pts, submitted by zx2c4 himself, Mar 2020), 'Response to WireGuard: great protocol, but skip the Mac app' (926 pts, 376 comments, Jan 2021 - Donenfeld's mailing-list rebuttal), 'WireGuard Gives Linux a Faster, More Secure VPN' (Wired, 741 pts, Mar 2020), 'Wireguard FPGA' (640 pts, Oct 2025), 'GotaTun - Mullvad's WireGuard Implementation in Rust' (632 pts, Dec 2025), 'Tell HN: Russia has started blocking OpenVPN/WireGuard connections' (439 pts, Jan 2024), self-host classics ('Setting up a home VPN server with WireGuard' 616 pts 2019; 'Build your own private WireGuard VPN with PiVPN' 552 pts 2023), and the Apr 2026 Microsoft signing-resolution thread (549 pts).
Fetched 2026-11-03 (HTTP 200; the body-search variant with body= parameter returned HTTP 400, so the plain listing endpoint was used): 25 recent r/WireGuard comments covering self-host threat-model questions (public WiFi/MITM visibility of your home IP), CGNAT/roaming pain on cellular (AT&T stale tunnels, tower-to-tower IP changes, keepalive workarounds), router performance measurements (BPI-R4 1.6 Gbps CPU-bound vs 2.4 Gbps on x86, IPsec comparison), community-built key-connect logging on OpenWrt, internal AD/DNS over the tunnel, and the TCP-fallback question.
Fetched 2026-11-03 (HTTP 200): 735 stars, 325 forks, GPL-2.0, language C, last push 2026-05-06; description reads 'Mirror only. Official repository is at https://git.zx2c4.com/wireguard-tools'; has_issues:false, has_discussions:false, has_pull_requests issue-creation disabled - the official GitHub presence deliberately redirects all bug reports to the mailing list, confirming the project's single-maintainer, mailing-list-driven workflow (open issue count field reflects the disabled tracker).
KI-Fakten-Report - alles, was wir wissen, komprimiert
Erstellt von Qwen3 am 2026-11-03 aus unserer Faktendatenbank plus den verlinkten Quellen. Er fasst zusammen - er fügt keine Fakten hinzu. Prüfe alles Wichtige gegen die verlinkten Quellen.
Bottom line: This is not a VPN service but a protocol you run yourself. You are the provider: no third party, no logs by design, but full responsibility for setup, key management and server upkeep. Performance and security are excellent, but it offers no built-in obfuscation or censorship circumvention.
The logging truth: No logs exist unless you configure them - logging is structurally impossible at the protocol level. Jurisdiction is irrelevant: there is no operator to subpoena, only your own server and keys. The evidence is formal verification (Tamarin, eCK, CryptoVerif), not audits of a company.
Pricing reality: The software is free. You pay only for the hardware - typically $5/month for a VPS or a few dollars per year for a low-end box. No renewal traps, no billing - just your infrastructure costs.
What reviewers say vs what users say: Reviewers (Ars, Cloudflare) praise its elegance, speed, and minimalism - calling it a “work of art” and future standard. Users agree on security and performance but highlight usability pain: split tunneling is clunky, per-process routing requires workarounds, and Windows depends on Microsoft’s signing. No conflict - both sides align on strengths and trade-offs.
Who runs it: Jason A. Donenfeld (ZX2C4) alone owns the code, trademark, and project direction. GitHub is a mirror; development happens via mailing list. This ensures focus but creates a single point of failure.
Quellen & wie dieser Review entstand
Jede externe Quelle, die auf dieser Seite verwendet wird, mit dem Abrufdatum und ihrer Belegklasse [A]-[D] (A = Primär-/Betreiberquelle, B = seriöse Presse/Forschung, C = Community, D = eigene Messungen). Methodik: wie wir verifizieren. Quellen verschwinden oder ändern sich - falls ein Link tot ist, sag uns über die Kontaktseite Bescheid.
Evidence classes on this page:[A] A: 6[B] B: 7[C] C: 4[D] D: 0(D stays empty until our own test phase)
The most credible self-hosting on-ramp in the VPN space, built by and for people inside the censorship: the app is free and open source, you connect it to your…
auditiertOpen Source
Einstieg ca. 4,40 € /mo
Cyprus (EUPHORIATECH LIMITED, Nicosia, reg HE 484287 per site footer, verified 2026-11-02; IP rights in Portugal with Amnezia LDA, ops in Estonia) - for self-hosted users the operative jurisdiction is wherever their own VPS is hostedselbst gehostetes vpn vor 3 Tg.
The gold standard for connecting your OWN devices, and a poor substitute for a consumer VPN - which is exactly what it says on the tin. Tailscale is a…
AuditOpen Source
Einstieg ca. 7,10 € /user/mo
Canada - Tailscale Inc., Toronto, Ontario (Wikipedia, Bloomberg); a Five Eyes member country; privacy policy names processing locations in Canada, Germany, the US and the UKselbst gehostetes vpn vor 3 Tg.
The incumbent of self-hosted business VPNs, and still a safe pick in 2026 - with one honest fork in the road. Access Server is the polished, supported way to…
AuditOpen Source
Einstieg ca. 6,20 € /mo
United States - OpenVPN Inc., Pleasanton, California (about page fetched 2026-11-03); a Five Eyes member countryselbst gehostetes vpn vor 42 Std.
Noch keine Kommentare - sei der Erste. Das Posten läuft durch einen kurzen Proof-of-Work in deinem Browser (Anti-Spam), kein Konto nötig.