Der Goldstandard, um DEINE EIGENEN Geräte zu verbinden, und ein schlechter Ersatz für ein Consumer-VPN – genau das, was der Name verspricht. Tailscale ist ein WireGuard-Mesh-Koordinator: Der Datenverkehr fließt geräteübergreifend mit Ende-zu-Ende-Verschlüsselung, der serverseitige, closed-source-Koordinationsdienst sieht Metadaten zu Geräten, Schlüsseln und Verbindungen einschließlich der Information, welche Knoten miteinander kommunizieren, und Exit-Nodes sind deine eigenen Maschinen, es sei denn, du zahlst für das Mullvad-Add-on. Die kostenlose Personal-Version (6 Nutzer, unbegrenzte Geräte, verifiziert am 2026-11-02 als aktiv) ist tatsächlich großzügig und wird von Homelab-Communities geliebt. Ehrliche Einschränkungen: keine öffentliche Prüfung der geschlossenen Steuerungsebene (SOC-2- und Latacora-Berichte nur auf Anfrage), Client-Logs werden standardmäßig an Tailscale übertragen, sofern nicht deaktiviert, Unternehmenszahlungen sind gemäß den Geschäftsbedingungen nicht erstattungsfähig, und die im Oktober 2026 erfolgte unkoordinierte „Tailworm“-Veröffentlichung (11 SSH-Schwachstellen, Root-Socket-Forwarding-Eskalation, behoben in v1.104.4) zeigte, wie schnell ein vertrauenswürdiges Tool dringend gepatcht werden muss. Nutzer, die Tailscale vollständig selbst hosten, umgehen die Vertrauensfrage über Headscale, den alternativen Open-Source-Kontrollserver – den Tailscale duldet, anstatt ihn selbst zu entwickeln. Qualität der Dossier-Daten: Alle Seiten des Betreibers, GitHub-Dateien, Wikipedia, die unabhängige Bewertung, Nachrichten, der Tailworm-Bericht und Community-Archive wurden am 2026-11-02 live von dieser Seite abgerufen; die Koordinierungs-Backend-Infrastruktur selbst kann von niemandem außerhalb des Unternehmens unabhängig verifiziert werden.
AuditOpen Source3 rote FlaggenFakten verified - operator pages (pricing, security, privacy policy, how-tailscale-works, exit-nodes docs, security bulletins, SSH investigation page, SSH findings blog, Series C blog), GitHub README + BSD-3 LICENSE + issue 498, Wikipedia, The Proof Desk review, Network World, Tailworm report, HN Algolia and Reddit arctic-shift archives all fetched live 2026-11-02; BleepingComputer and The Hacker News returned 403 (Cloudflare) and are cited from search-result snapshots only
October 2026 'Tailworm' incident: Cyberdione Labs published 11 findings in tailscaled v1.104.2 and headscale v0.29.5 with uncoordinated disclosure; root-privileged SSH Unix-socket forwarding could reach the Docker socket and tailscaled local API; fixed in v1.104.4 within days (fast response, but SecurityWeek and BleepingComputer noted a stolen device key stays valid until deleted at the control plane - reimaging the machine does not revoke it)
Five Eyes jurisdiction (Canada) plus a closed-source control plane: this is the whole argument for Headscale, NetBird or plain WireGuard if your threat model includes the operator itself
Heavy VC trajectory: $275M total funding and a $1.5B valuation (Bloomberg, 2025-04-08), first acquisition Border0 (2026-03-17, BetaKit/Bloomberg) and an enterprise pivot toward PAM and AI governance - the homelab product is now the top of a commercial funnel, though the free tier has so far been preserved and even widened (3 to 6 users in 2026)
Review
Entwurf von Qwen3, faktengeprüft von der vpnvergleich-Redaktion · Review-Version 3 · Text aktualisiert 2026-11-02 · Fakten Stand 2026-11-02 · wie wir verifizieren
Ehrlichkeits-Hinweis: wir haben keine eigenen Tests zu Tailscale (managed WireGuard mesh) gelaufen (Leak-Tests, Tempo, Kill Switch). Alles auf dieser Seite ist quellbasierte Meta-Recherche mit datierten Links. Sobald wir testen, erscheinen die Ergebnisse hier und im Änderungsprotokoll.
Overview
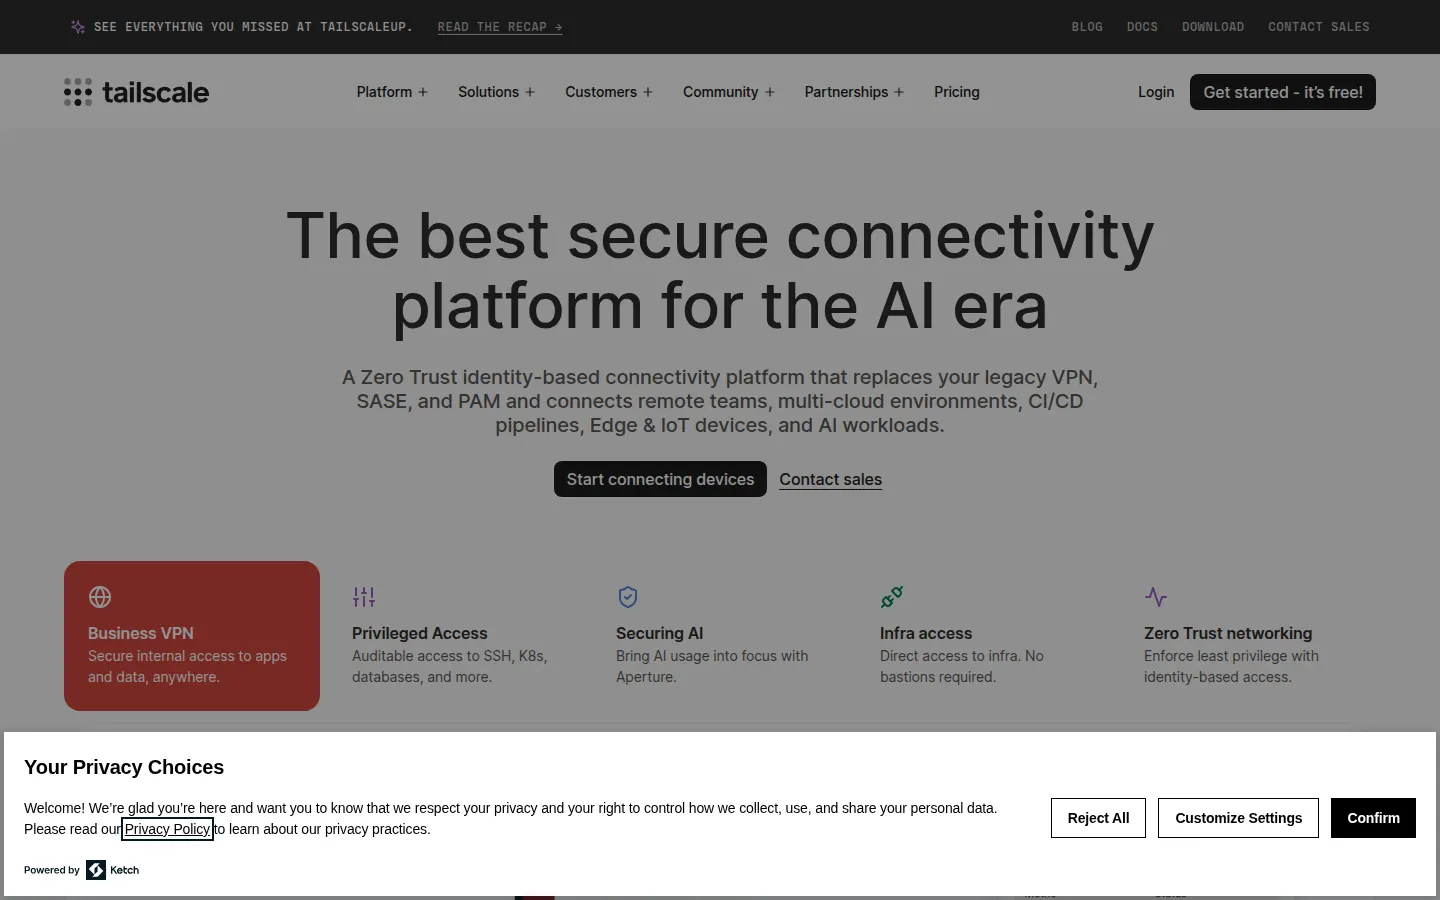
Tailscale (managed WireGuard mesh) homepage - live capture 2026-09-29
Tailscale is a hosted WireGuard mesh coordination service that simplifies private network setup between your own devices. It’s not a consumer VPN - traffic stays end-to-end encrypted, but the closed-source control plane collects connection metadata. Operated by Tailscale Inc. in Canada (a Five Eyes country), it's ideal for self-hosters and remote access, but you must trust the operator with device and peer relationship data.
Logging & privacy
Tailscale claims it cannot see your traffic due to WireGuard’s end-to-end encryption, and DERP relay code is open source to verify they forward only ciphertext. However, the coordination server - closed source - collects metadata: device names, public keys, IP addresses, OS types, timestamps, and Inter-Node Traffic Logs showing which devices communicate and approximate data volumes. This is a "policy-only" logging claim with no public audit of the control plane. While SOC 2 Type II and Latacora audits exist, they’re available only on request. Jurisdiction in Canada raises concerns for high-risk users, and there’s no warrant canary.
Pricing & the renewal trap
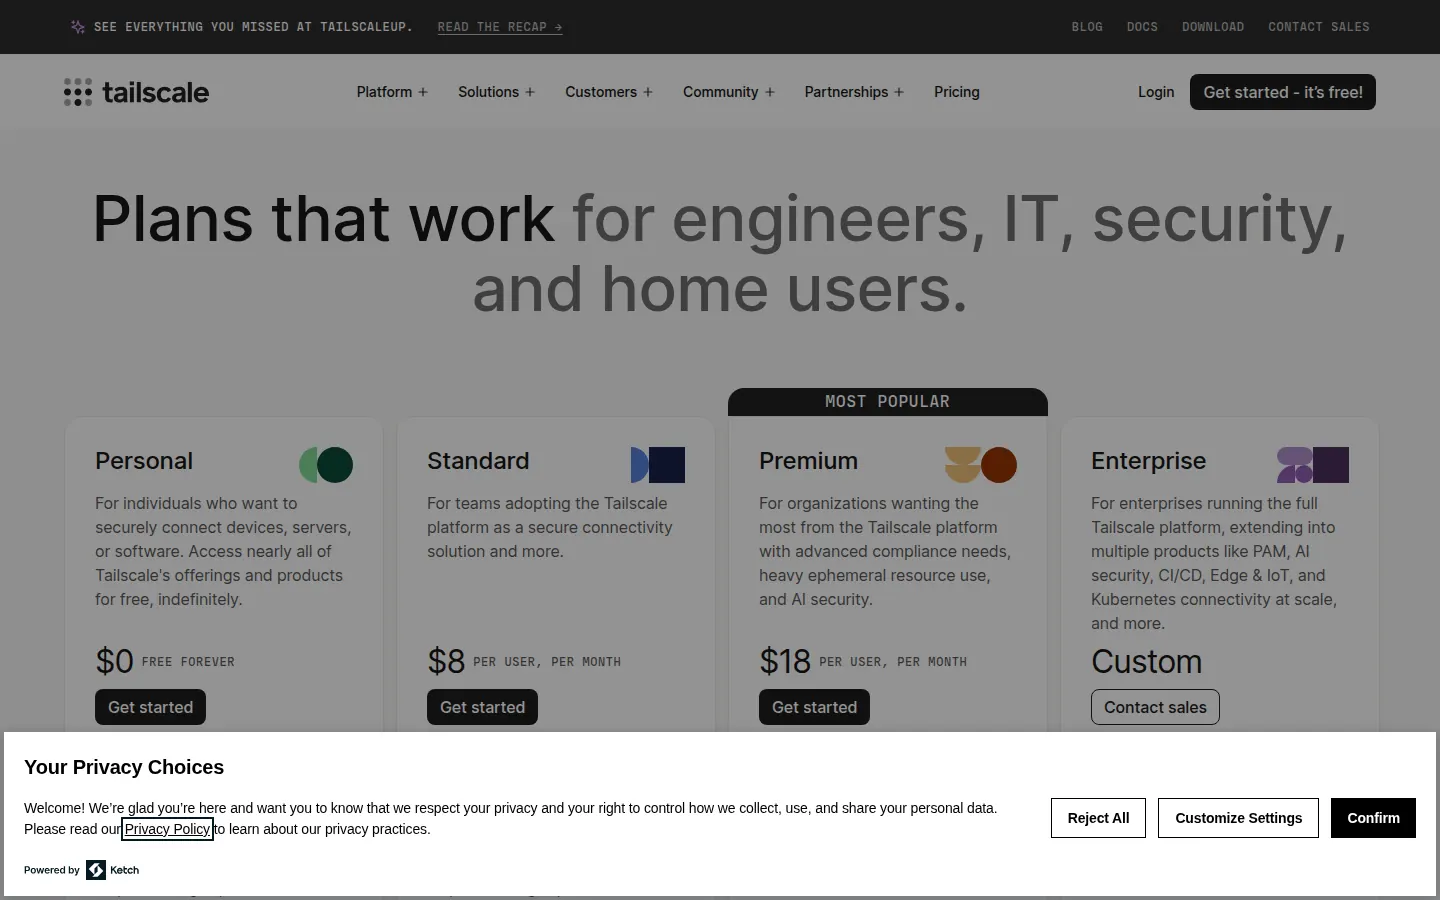
Tailscale (managed WireGuard mesh) pricing page - live capture 2026-09-29
Tailscale’s Standard business plan costs $8 per user per month, with no change at renewal - the derived renewal ratio is 1. There’s no refund window (0 days), and payments are non-refundable per the Terms of Service. The free Personal plan supports up to 6 users and unlimited devices, verified live in 2026. No multi-year pricing or intro discounts exist, so the renewal trap is neutralized by flat pricing. Payment is fiat-only; crypto is not accepted.
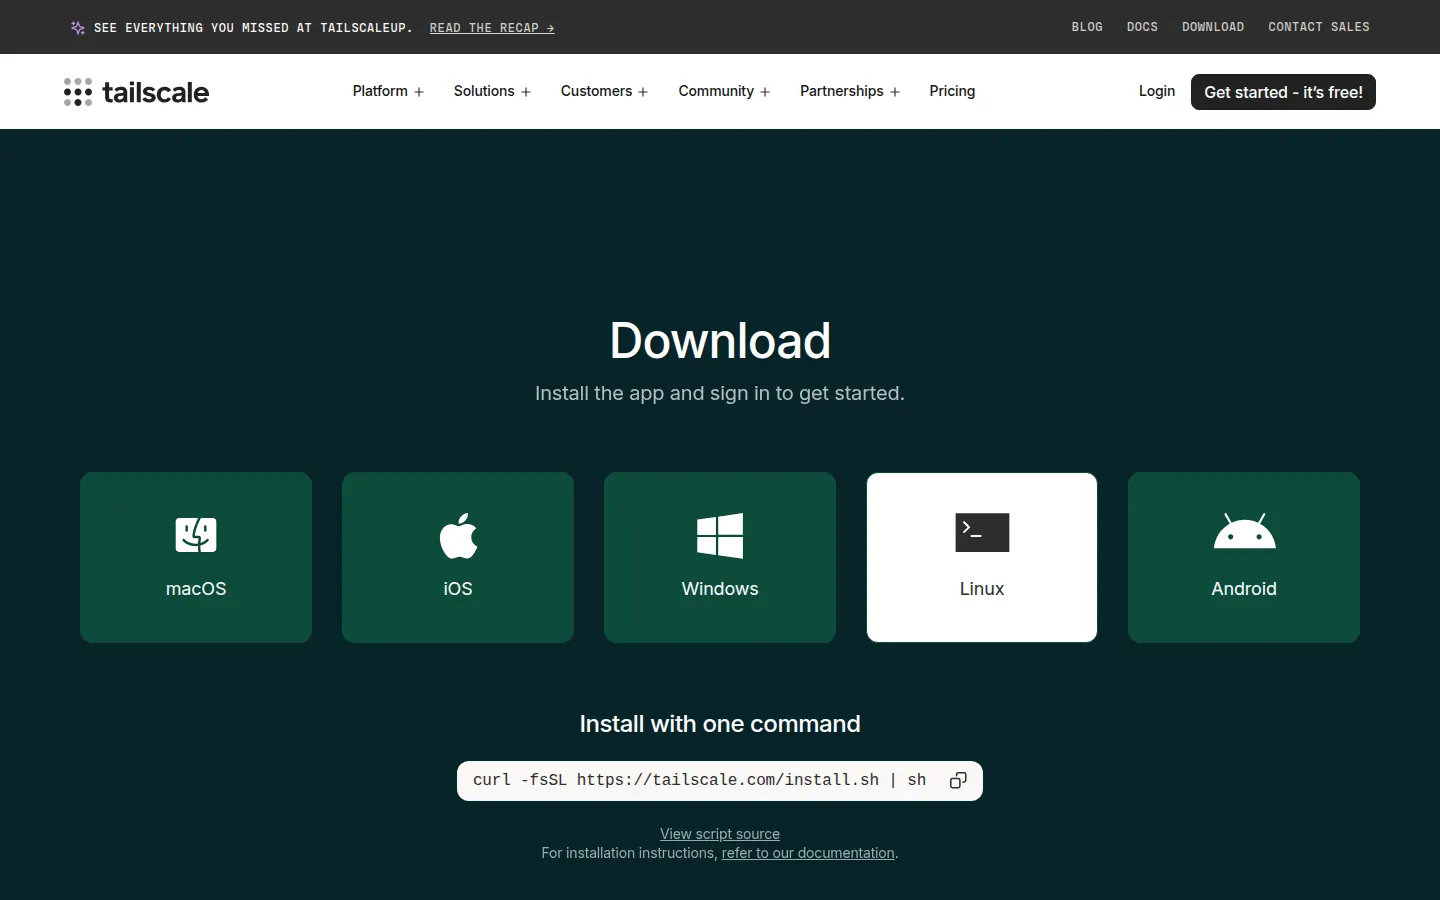
Built on WireGuard, Tailscale offers split tunneling, peer-to-peer routing, and optional exit nodes (your own devices or Mullvad add-on). It supports Windows, Mac, Linux, Android, iOS, and routers. No multihop, dedicated IPs, Tor over VPN, or obfuscation. Servers and countries count are irrelevant - this is a mesh, not a traditional VPN network. P2P is enabled by default; streaming geo-unblocking isn’t supported. No kill switch is documented. We haven’t run performance tests, but WireGuard ensures low latency when direct P2P works; DERP relays handle NAT traversal with minimal overhead.
Ownership & track record
Ownership details are not publicly disclosed. Tailscale Inc., based in Toronto, has raised $275M in funding and acquired Border0 in 2026, signaling an enterprise pivot. The 2026 "Tailworm" incident revealed 11 vulnerabilities, including root-level SSH escalation, though exploitation required prior access to an authorized device. Fixes shipped quickly, but the uncoordinated disclosure and lack of public audit for the control plane remain concerns. Data quality is verified across operator pages, GitHub, Wikipedia, and community archives, but the core coordination server remains unverifiable by independent parties.
Censorship resistance
Tailscale does not offer obfuscation and is not designed for use in heavily censored environments like China or Iran. Its reliance on direct UDP for WireGuard and DERP relays makes it easily detectable and blockable. Without traffic masking, this tool should not be used where circumvention of state-level censorship is required. Alternatives like Shadowsocks or obfuscated WireGuard setups are more suitable.
Verdict
Tailscale is the best choice for securely connecting your own devices with minimal setup - perfect for homelabs, NAS access, or remote work. It’s not a privacy tool for anonymity or streaming. You pay for convenience, not secrecy, and must trust Tailscale with metadata. The free tier is generous, pricing is flat, and the ecosystem is well-supported. No evidence suggests Tailscale pays review sites to promote it.
++ Was hält stand
Kostenloser Persönlicher Tarif: bis zu 6 Nutzer und unbegrenzte Geräte, keine Karte erforderlich (aktuelle Preisseite 2026-11-02)
Ende-zu-Ende-WireGuard-Verschlüsselung; private Schlüssel verlassen niemals die Geräte; DERP-Relays leiten nur Chiffretext weiter (Sicherheitsseite des Betreibers abgerufen 2026-11-02)
Open-Source-BSD-3-Clients und DERP-Relay-Code sowie ein florierender Third-Party-Selbsthost-Pfad über Headscale
Reibungslos: SSO-Anmeldung, NAT-Punching, das einfach funktioniert, und das Tailnet bleibt auch bei Ausfall des Koordinationsservers funktionsfähig (Betreiberdokumentation)
Der Mullvad-Exit-Knoten-Zusatz für 5 $/Monat pro 5 Geräte nutzt einen tatsächlich respektierten no-logs-Betreiber
Sicherheitstransparenz: öffentliche CVE-ähnliche Sicherheitsbulletins, und die Reaktion auf Tailworm im Oktober 2026 erfolgte von der Offenlegung bis zum Patch-Release in etwa 4 Tagen
-- Worauf du achten solltest
Der quelloffene Koordinationsserver sieht dein Geräteinventar, öffentliche IPs und welche Knoten mit welchen verbunden sind – Vertrauen in Tailscale Inc. ist strukturell
Kein öffentlicher Audit-Bericht: SOC 2 Type II und laufende Latacora-Audits nur auf Anfrage oder nur für Kontoinhaber zugänglich
Kein Anonymitäts-VPN: kein gemietetes Servernetzwerk, Exit-Knoten sind deine eigenen Maschinen, Streaming und Geo-Entsperren sind nicht vorgesehen
Zahlungen sind gemäß den Allgemeinen Geschäftsbedingungen nicht kündbar und nicht rückerstattbar (abgerufen 2026-11-02)
Client-Sitzungsprotokolle werden standardmäßig an log.tailscale.com gesendet, es sei denn, du deaktivierst dies mit --no-logs-no-support
Funktionsexpansion seit 2024 (PAM, Aperture AI Gateway, DNS-Filterung) – die Community warnt, dass der einfache Kern unter Enterprise-Erweiterungen begraben wird
Preis-Realitätscheck
Einführungspreis
ca. 7,10 € /user/mo · Verlängerung ca. 7,10 €/Mon.
Verlängerungspreis
ca. 7,10 €/Mon.
Hinweise
Persönlicher Tarif ist dauerhaft kostenlos (aktuelle Preisseite 2026-11-02). Business: Standard 8 $ pro Nutzer/Monat, Premium 18 $ pro Nutzer/Monat, Enterprise individuell. Zusatzoptionen: Mullvad-Exit-Knoten 5 $/Monat pro 5 Geräte, zusätzliche getaggte Ressourcen je 1 $/Monat. Allgemeine Geschäftsbedingungen (abgerufen 2026-11-02): Zahlungen sind „nicht kündbar, nicht übertragbar, nicht rückerstattbar“.
Der Geldfluss - was Testportale mit dieser Empfehlung verdienen
Affiliate-Status noch nicht verifiziert
Sollten wir dieses Programm joinen, wird jeder Link hier rel="nofollow sponsored" und läuft über /go/. Bis dahin zeigen unsere Links direkt auf die Anbieter-Website, ohne jegliches Tracking. Die Ranking-Logik kann Affiliate-Felder physisch nicht lesen - hier der Beweis.
On the website
Captured by our screenshot bot from the live site (or its public archive). A capture is evidence of what the page showed at capture time - not an endorsement.
Tailscale (managed WireGuard mesh) homepage - live capture 2026-09-29Tailscale (managed WireGuard mesh) pricing page - live capture 2026-09-29Tailscale (managed WireGuard mesh) apps / download page - live capture 2026-09-29
Bevor du zahlst: prüfe den Verlängerungspreis, das Erstattungsfenster und ob ein günstigerer oder Gratis-Weg deinen Anwendungsfall abdeckt - die ehrliche Checkliste.
Stand unserer Prüfungen: 2026-11-02. Tailscale (managed WireGuard mesh) erreicht 4.9/10 in unserem gewichteten Review. Wir haben 3 rote Flaggen vermerkt (oben aufgelistet). Nutzerberichte, Eigentum und die Vorfallhistorie sind mit datierten Quellen im Meta-Review unten dokumentiert.
What do I actually get with Tailscale?
You get a managed WireGuard mesh that connects your devices securely with end-to-end encryption. The free plan allows 6 users and unlimited devices; business tiers add policy controls and support. Traffic flows peer-to-peer or via DERP relays, and exit nodes let your devices route through your own servers.
What is the renewal price and total cost over three years?
The monthly rate is $8 per user, with no change at renewal - the renewal ratio is 1. Since pricing is flat and recurring, the three-year cash total is not precomputed, but you’ll pay $8 per user each month indefinitely.
What proof is there for Tailscale’s no-logs claim?
There is no independent public audit of the closed-source coordination server. The logging claim is "policy-only" - Tailscale says it collects only metadata (device info, connection logs), but this can’t be independently verified. DERP relay code is open source and doesn’t log, and SOC 2 reports are available only on request.
Can I use Tailscale in a censored country like China or Iran?
No. Tailscale lacks obfuscation and uses standard WireGuard traffic patterns that are easily detected and blocked. It is not suitable for bypassing state-level censorship. Use tools designed for obfuscation, like Shadowsocks or customized WireGuard with cloaking.
Can I pay anonymously or sign up without an identity?
No. You must sign up using an email or SSO identity (Google, GitHub, etc.). True anonymity isn’t possible on the hosted service. For anonymous-adjacent use, self-host Headscale with a private auth backend or run plain WireGuard without a coordinator.
What happens if Tailscale shuts down or gets acquired?
If Tailscale shuts down, hosted users lose coordination. Self-hosted Headscale users remain unaffected. The client is open source (BSD-3), but the control plane is not. Acquisitions (like Border0) suggest enterprise focus, but the free tier has been preserved and expanded so far.
What’s the honest free or cheap alternative?
Use Headscale - a fully open-source, self-hosted Tailscale-compatible control plane - or plain WireGuard for full control. For consumer privacy, consider Mullvad (audited no-logs, flat pricing) or IVPN (independent, transparent). These cost money but don’t rely on trusting a closed coordinator.
Der Meta-Review: was das Internet über Tailscale (managed WireGuard mesh) sagt
Wir erwarten nicht, dass du uns vertraust. Dieser Review ist ein Meta-Review: unten siehst du, was andere Testportale behaupten - mit ihren Interessenkonflikten gekennzeichnet -, was Nutzer auf Reddit und in Foren berichten und wer Tailscale (managed WireGuard mesh) wirklich betreibt. Jede Behauptung verlinkt ihre Quelle, damit du sie selbst prüfen kannst.
Was andere Tester sagen (1)
Jede Quelle trägt ein Konflikt-Label aus unserer Testportal-Datenbank. „Affiliate-finanziert“ heißt: Die Seite verdient mit, wenn du kaufst, was sie empfiehlt. Kritische Stimmen nehmen wir bewusst auf.
Fetched 2026-11-02: small independent editorial review (monetization unknown). Honest scoping: Tailscale is 'not a VPN in the sense most VPN reviews use the word'. Likes the generous free plan and E2E encryption; dislikes the closed-source coordination server that sees device-to-device metadata, client logs streaming to Tailscale by default, non-refundable payments, and no public audit report (SOC 2 on request). Verdict: easiest way to connect your own devices; wrong tool for hiding your IP or streaming.
Was Nutzer sagen (6)
Reddit, Foren, HN - paraphrasiert und verlinkt, nie aus dem Kontext gerissen. Anekdoten, keine Beweise - aber Erstattungsbeschwerden und Leak-Reports sind das beste Frühwarnsystem, das dieser Markt hat.
Fetched 2026-11-02 (25 comments): homelab texture - Plex/Jellyfin served over tailnets, subnet routers, Serve vs Funnel security advice, ephemeral-node Docker troubleshooting, awareness of the Tailscale SSH vulnerabilities via the official r/Tailscale post, distrust of third-party UIs.
Fetched 2026-11-02 (15 comments): Tailscale as the default way to close public exposure after Plex/Nextcloud zero-days; binding containers to tailnet IPs; 'Headscale can be used if you want 100% self-hosted'; one user moving public-facing services to SSO + Cloudflare instead.
Fetched 2026-11-02 (15 comments): r/VPN regulars recommend Tailscale exit nodes as the free way to get a home IP while traveling; one sarcastic 'beautiful disclosure' jab after the SSH patch; exit node on Apple TV or Pi suggested.
Thread page fetched 2026-11-02 (HTTP 200), comments via HN Algolia API: accurate framing that the flaws require an already-authorized tailnet peer, Headscale users affected too (bug in tailscaled), 'nearly everyone uses zero advanced features', plug for Headscale/NetBird, praise for the fast fix.
Fetched 2026-11-02 via GitHub API: the original community request to open-source the coordination server ('it would be even more perfect if the server was open-source'), opened June 2020, closed December 2022 without the server being open-sourced; the issue that seeded years of Headscale advocacy.
Fetched 2026-11-02 (9,881 comment hits for tailscale; 2,276 for headscale): HN treats Tailscale as core homelab/devops infrastructure - recommended by default, incident discussed with technical precision, Headscale normalized as the self-host answer.
KI-Fakten-Report - alles, was wir wissen, komprimiert
Erstellt von Qwen3 am 2026-11-02 aus unserer Faktendatenbank plus den verlinkten Quellen. Er fasst zusammen - er fügt keine Fakten hinzu. Prüfe alles Wichtige gegen die verlinkten Quellen.
Bottom line: Tailscale is the easiest way to connect your own devices securely via WireGuard, with a generous free tier (6 users, unlimited devices). It is not a consumer VPN and does not hide your IP from websites or provide anonymity. Traffic is end-to-end encrypted, but the coordination server sees metadata about which devices talk to which, including public IPs and connection patterns.
The logging truth: Tailscale claims it cannot read your traffic due to WireGuard encryption, which is accurate - payloads are safe. However, it admits to collecting device metadata, connection logs, and traffic statistics (Inter-Node Traffic Logs), stored in Canada, the US, Germany, and the UK. This metadata collection is confirmed in its privacy policy and security page; the closed-source control plane cannot be independently verified, and audits (SOC 2, Latacora) are not public.
Pricing reality: The Personal plan is $0 forever with solid limits (6 users, unlimited devices). Business tiers start at $8/user/month with no intro discount, and payments are non-refundable per the Terms. No billing traps beyond the hard renewal terms - pricing is flat and transparent, but you lose money if you cancel.
What reviewers say vs what users say: Independent reviewers like The Proof Desk stress Tailscale’s misclassification as a VPN, praising its encryption and free tier but criticizing the closed control plane and default client logging. Users on Reddit and HN overwhelmingly praise it for homelab and self-hosting use, though the October 2026 Tailworm incident sparked debate - some dismissed the risk (required prior access), while others questioned trust in the platform, showing a split between operational utility and security paranoia.
Who runs it: Tailscale Inc., based in Toronto, Canada, founded in 2019, operates the service. It has raised $275M and is pivoting toward enterprise identity and AI governance, acquiring Border0 in 2026. The company tolerates self-hosted alternatives like Headscale but keeps its control plane closed, making full trust unavoidable for hosted users.
Quellen & wie dieser Review entstand
Jede externe Quelle, die auf dieser Seite verwendet wird, mit dem Abrufdatum und ihrer Belegklasse [A]-[D] (A = Primär-/Betreiberquelle, B = seriöse Presse/Forschung, C = Community, D = eigene Messungen). Methodik: wie wir verifizieren. Quellen verschwinden oder ändern sich - falls ein Link tot ist, sag uns über die Kontaktseite Bescheid.
Evidence classes on this page:[A] A: 11[B] B: 8[C] C: 6[D] D: 0(D stays empty until our own test phase)
The most credible self-hosting on-ramp in the VPN space, built by and for people inside the censorship: the app is free and open source, you connect it to your…
auditiertOpen Source
Einstieg ca. 4,40 € /mo
Cyprus (EUPHORIATECH LIMITED, Nicosia, reg HE 484287 per site footer, verified 2026-11-02; IP rights in Portugal with Amnezia LDA, ops in Estonia) - for self-hosted users the operative jurisdiction is wherever their own VPS is hostedselbst gehostetes vpn vor 3 Tg.
The incumbent of self-hosted business VPNs, and still a safe pick in 2026 - with one honest fork in the road. Access Server is the polished, supported way to…
AuditOpen Source
Einstieg ca. 6,20 € /mo
United States - OpenVPN Inc., Pleasanton, California (about page fetched 2026-11-03); a Five Eyes member countryselbst gehostetes vpn vor 41 Std.
The most polished way to hand censorship-resistant access to people who cannot configure a VPN: a few clicks in the Outline Manager builds a Shadowsocks server…
AuditOpen Source
Einstieg ca. 2,70 € /mo
United States - Outline Foundation, 30 N Gould St. #57975, Sheridan, Wyoming (contact address in Terms of Service and on the Google Play developer listing); ToS governed by Wyoming law. The software itself has no jurisdiction: the operative jurisdiction for a self-hosted user is wherever their rented VPS is located and the laws governing their cloud provider.selbst gehostetes vpn vor 2 Tg.
Noch keine Kommentare - sei der Erste. Das Posten läuft durch einen kurzen Proof-of-Work in deinem Browser (Anti-Spam), kein Konto nötig.